


Company news
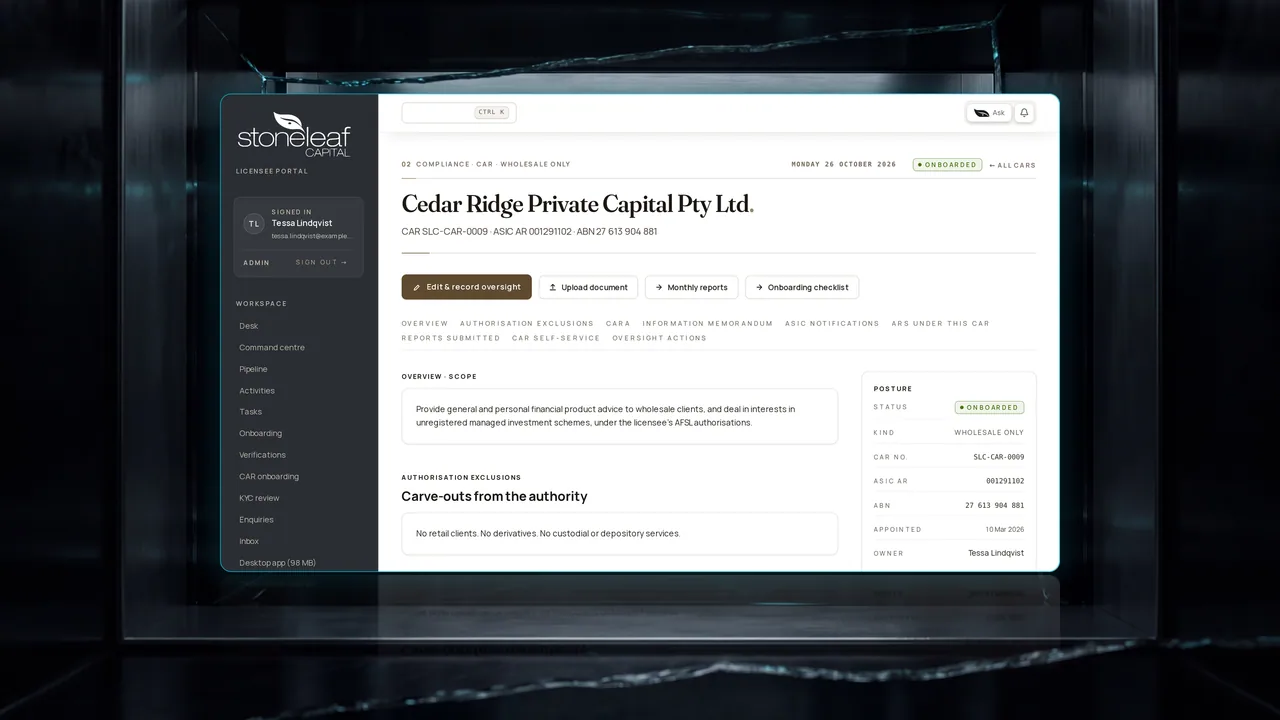
Stone Leaf Capital portal release: a CAR representative area, board minutes and named regulator owners
An area for authorised representatives, board minutes under e-signature and an owner for every regulator duty.
Black Shard


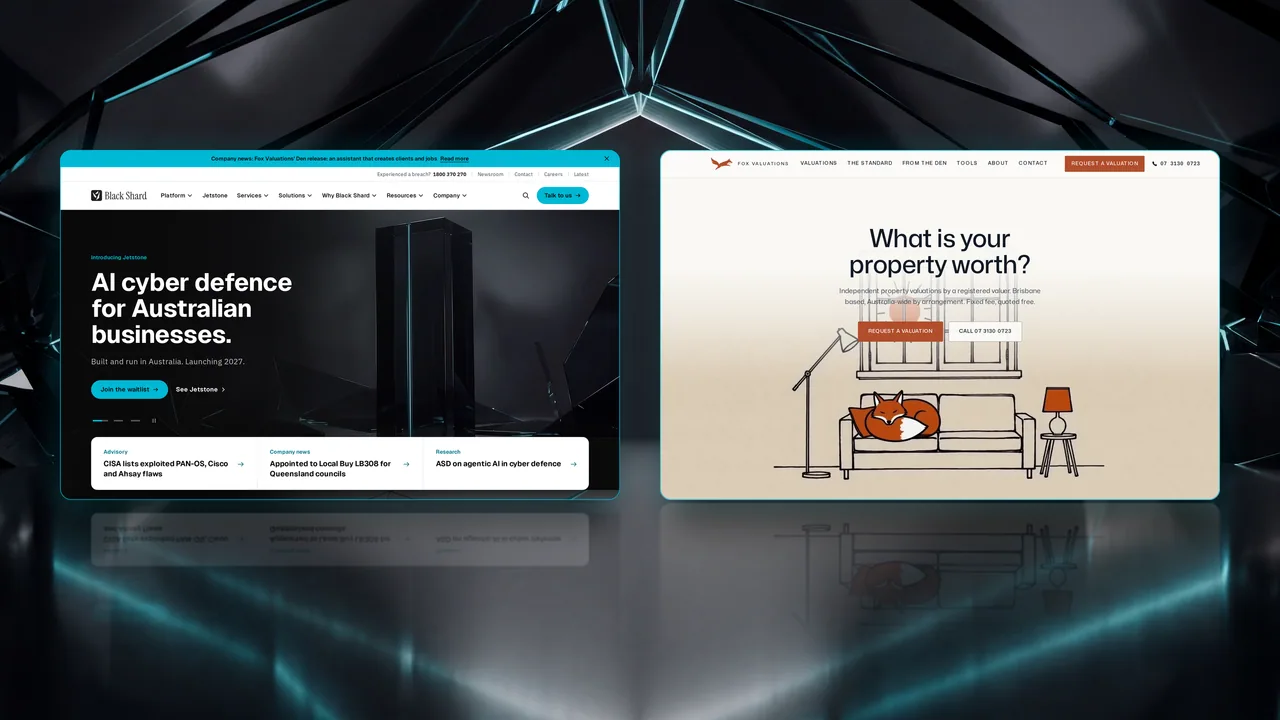
The Den, built and run for Fox ValuationsShown with sample data
Read the case studyThe attacks in our advisories reach Australian firms through the same few doors: an exposed edge device, a stolen password, a backup server left on the network. The flaws behind them are often exploited before a fix ships. Our security monitoring has analysed more than 476 million security events since 1 Oct 2026.
A few of our case studies, among the many systems we build, host and secure today.


Legal
The firm runs intake, conflicts, trust oversight and AML/CTF from one portal.
A new release of the portal ships every week.
 Shown with sample data
Financial services
Staff, investors and the board work from one portal inside the licence perimeter.
Every investor is identity-checked through InfoTrack before they can proceed.

Health
Specialists run notes, letters, orders and billing from one app.
Available in 174 App Store territories and 178 Google Play countries.

Health
The clinical site and the practice’s ICT now sit with one team.
A 19-page clinical website, migrated with zero outage.


Nominated twice on Awwwards, for our own site and for the Fox Valuations site we built. The CyberCert certificate and the Xero listing verify online; the panel records go out with our tender responses.
Also on the record

CyberCert
16 Jun 2026 to 17 Jun 2027
Local Buy
Appointed 23 Oct 2026
NSW Government
Registered 14 Oct 2026
Victorian Government
23 Oct 2026 to 22 Oct 2028
Own estate
Assessed September 2026
Reports and whitepapers
Report
OAIC figures of 6 Jul 2026, read 26 Oct 2026
Jetstone at the core. Practitioners who test, assure and respond around it. The engineering that builds and runs it.
The agent
Detect and respond
Test and assure
Build and run
Practitioners
Where Jetstone will run
Built on and integrated with
 Microsoft 365
 Microsoft Azure
 Microsoft Entra ID
 Microsoft Intune
 Microsoft Defender for Endpoint
 Microsoft Teams
 SharePoint




Responders stop an intrusion spreading today, and Jetstone will watch your devices and sign-ins.
Explore detect and respond
Stops an attacker finding the way in before you do.
Explore test and assure
Stops the systems you run on falling behind on patches, backups and uptime.
Explore build and runThe engineering and security work behind the software we build and run.
Analysed by our own security monitoring, the record our responders work from in an incident.
Our security monitoring, since 1 Oct 2026
Written and maintained by our own team, across client systems and our own products.
Non-blank lines in the repositories we own
Tests run before a release ships, so a change is checked before it reaches your people.
Tests in our repositories
Every change on record, so any line of a system traces back to who made it and why.
Git history across our product repositories, since 1 Jan 2026
Changes ship in small, reviewed steps, so each one is easy to check and to roll back.
Merged on GitHub, since 1 Jan 2026
Deploys go into the production systems we run every week.
Successful deploy and release runs, since 1 Jan 2026
Measured from our repositories and monitoring; last updated .
Jetstone
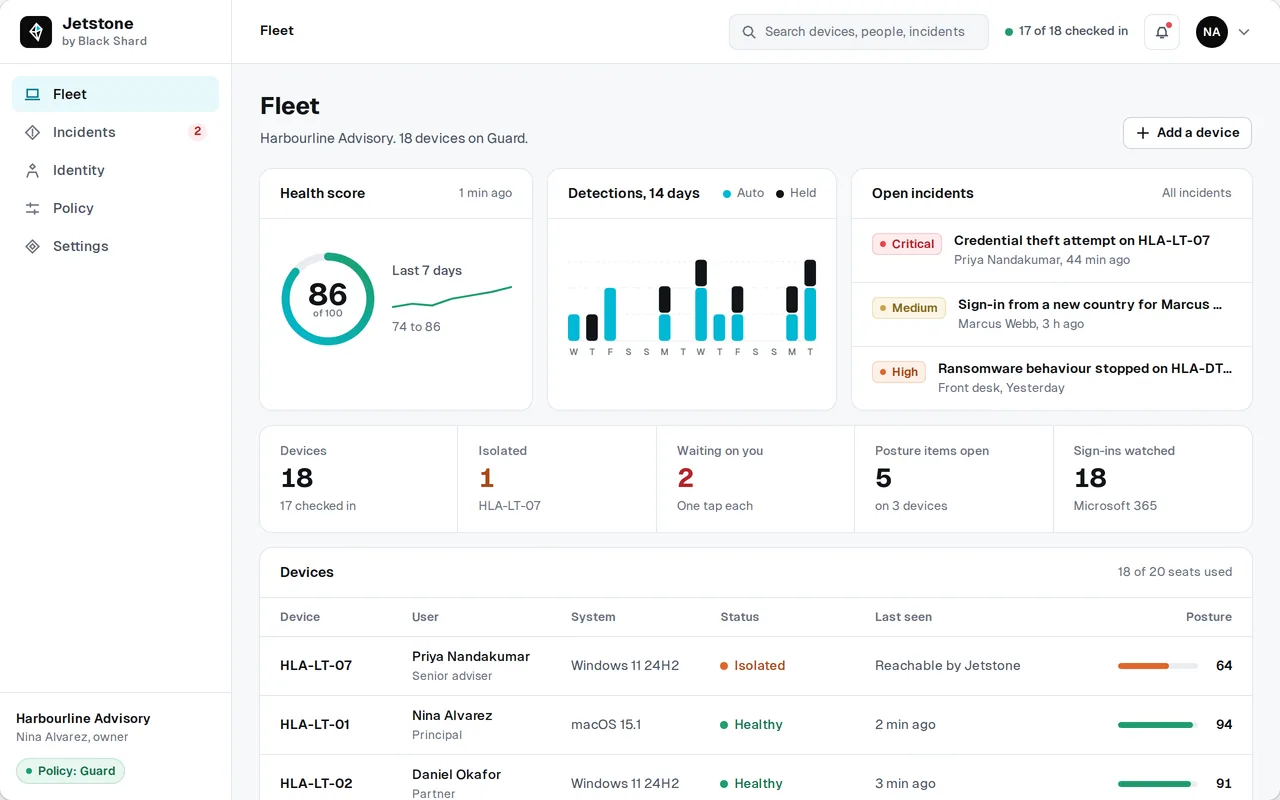
The console will fit a phone, and a Monday summary will cover the week. The waitlist is open now.
Fixed-scope offers with prices up front, and a free scoping call for everything else.
Software and security for the sectors we already build and run systems in.
 HealthClinical software and its security
 LegalTrust accounting and QLS obligations
 Financial servicesPortals for AFSL holders
 PropertyPractice systems and AML/CTF screening
 GovernmentCouncils and agencies
 Professional servicesTesting and managed ICT for firms
 Automotive and tradesWorkshop and dealer systems
 Motorsport and sport technologyRace-weekend decision software
 RecruitmentCandidate intake and placement
Releases from the firm, and advisories with the patched version and the first step.
Company news
An area for authorised representatives, board minutes under e-signature and an owner for every regulator duty.
Black Shard
Policy and regulation
Advisories
Talk to us about a test, a tender or Jetstone.
